Agentic network operations
Fleet operations, incident triage and sovereign troubleshooting, done by the agent you already use.
curl -fsSL https://yeet.cx | shLinux only | Manual install | Read the docs
Making your machines readable
With yeet, your live network traffic becomes the agent’s context for operating. Every connection, from your APIs to your containers, is a queryable surface to discover issues and optimize operations.
Claude Code v2.1.287
Opus 5 · Claude Max
~/code/api
- the name behind every TLS connection, read from the handshake, with no DNS to intercept
- raw packets on any interface, tunnels included, with the protocol tree and hex in the terminal
- HTTP, gRPC, SQL and Redis decoded off the wire, inside TLS too wherever the process uses OpenSSL
- every connection, in or out, tied to the process that made it and flagged when it leaves your network
- request rate, errors and latency per container, from inside its network namespace, no sidecar and no code change
Use yeet when you don’t know where the problem is
The DNS answer that pointed at the wrong host. The retry storm the logs never recorded. The container that opened a socket nothing in your dashboards names.
Network problems live below the layer your tools were built to watch. yeet lets the agent go read that layer directly, on the host where it happened, so the investigation ends where the logs run out instead of starting there.
“yeet has been one of the biggest keys to our development success at Kairos. When you’re building trading infrastructure, you need tools you can trust to keep up, and yeet has done that from day one.
The technology powering it is seriously impressive, and it’s versatile enough that we keep finding new ways to use it across our stack. It’s become a core part of how we build, and I’d recommend it to any team working on serious infrastructure.”
Use yeet for…
Fleet operations
Improve cluster health via ambient limit checks across clusters, setting up ephemeral triggers where things look suspicious.
Incident triage
Network incidents are the most challenging. Instead of digging through a thousand dashboards, generate specific views on the fly.
Sovereign troubleshooting
Pre-install yeet in on-prem deployments so customers can self-diagnose network issues and relay answers back.
You don’t pay per event
Your kernel doesn’t bill you per event, and neither do we.
Observability pricing scales with the events you emit, so the busier your network gets, the more it costs to look at it. yeet is one binary on your hosts reading the kernel directly. The count that drives everyone else’s bill is the count we never charge for, and you bring your own model.
It’s just Linux
yeet is a daemon on a Linux host. It runs the same on AWS, GCP and Azure, on Kubernetes nodes, in Docker or on bare metal.
Nothing about your networking changes: no sidecar, no proxy in the path, no CNI to swap. Your security or ours? Yours. yeet runs inside your account and your VPC, inherits the controls already there, and the data it reads stays on the host. Any agent that can run a command works with it.
 AWS
 GCP
 Azure
 Kubernetes
 Docker
 Prometheus
 Grafana
 Slack
 GPT
 Claude
 Jev
 Gemini
Security
Observation is read-only by default. Enforcement is opt-in.
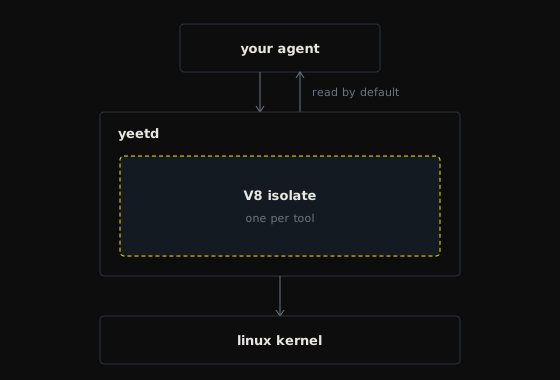
Each tool runs in its own V8 isolate with no filesystem, no arbitrary egress and no exec, and every eBPF program passes the kernel verifier before it attaches. yeet runs on your machines and keeps no copy of what your tools read. Cloud and sovereign on-prem deployments available.
Build custom infrastructure
With access to runtime system data and yeet’s build primitives, your agents become capable of building a new category of infrastructure tools. From protocol debuggers to test infrastructure, every new tool in your stack is now custom-built to your needs.
Agentic network operations in under 60 seconds
curl -fsSL https://yeet.cx | shLinux only | Manual install | Read the docs