What is yeet? The kernel primitive for programmable infrastructure

I started this gangsta' shit. And this is the motherfuckin' thanks I get?
It’s what you reach for when the dashboards say everything is fine, but the system clearly isn’t. Or when the firewall, sandbox or gateway you need doesn’t exist yet, and you’d rather build it than wait for it.
It’s built for the engineers who build infrastructure. People who live in htop, write clever one-liners with awk, and still have iptables rules from 2014 they’re afraid to touch. More and more, it’s also built for the agents those same people hand a terminal to.
Ok, that’s cool, but like… what is it?
yeet gives you kernel-level primitives for security, observability and networking. You write a script in JavaScript, start it with yeet run, and that script can load eBPF programs, watch and filter traffic, read live system state, and show you whatever it finds in your terminal or your browser. It’s a good abstraction on top of the kernel’s BPF subsystem, so normal people (and models) can use it without sacrificing their sanity to its black magic.
When something’s broken, exposed, or just being weird, you don’t want to dig through five dashboards or file a ticket with the network team. You just want to ask:
- “What is this service talking to, and should it be?”
- “Which process just dialed out to an IP nobody recognizes?”
- “Can I block that without redeploying anything?”
For years the answer was a different product for every question: a firewall appliance, a service mesh, an observability vendor, a sandbox. yeet is the thing those products are made of.
yeet gives you the power to build the exact tool your question needs, on the machine where the problem is, and throw it away when you’re done.
yeet is not about collecting everything forever. It’s about getting the right data, right now.
Because when pagers start going off at 3am and your systems are melting, you don’t need another dashboard. You need answers.
Nice, but after browsing around a bit I can’t really tell. Is it like a website? A package manager? A server? A CLI?
None of the above. It’s a primitive.
Think about what docker run did. Mount namespaces landed in Linux 2.4.19 in 2002, and most developers didn’t touch them until Docker wrapped them in one command in 2013. That command made containers something everyone could build on. CI runners, dev containers and Kubernetes all stand on containers today. Docker didn’t build your CI pipeline. It gave you the piece you build it from.
eBPF has been in Linux since 3.18 in 2014, and it can see almost everything the kernel does: every syscall, every packet, the functions inside a running binary. It can also decide what happens next: drop a packet in the NIC driver, refuse a connection, deny a file read. But writing it means C, kernel headers, and a verifier that rejects your program and explains why in BPF assembly. So most people never touch it.
yeet run is the one command for eBPF. So don’t judge yeet by the tools that ship with it. Judge it by what you can build on top of it.
Mask off: Let’s see what’s really underneath.
I. 🧱 yeet the daemon (yeetd)
This is the part that lives on each host, quietly waiting for a script to tell it what to look at. It’s what you are installing when you type that good old curl -fsSL https://yeet.cx | sh into your terminal.
Here’s what it does:
- Runs your scripts in an embedded V8 JavaScript engine, each one in its own isolate.
- Manages the lifecycle of BPF objects, including maps, programs and links, from load to cleanup.
- Models the whole machine as a graph of processes, sockets, containers, GPUs and sensors, all queryable through GraphQL.
- Streams data from kernel space to your script as it happens.
tl;dr yeetd does the dangerous, boring part. It holds root, talks to the kernel, and cleans up after you, so your script only has to say what it wants to see.
II. ⚡ yeet the runtime (yeet run)
One-off tools are cool, until you need to run them somewhere else, change them, or hand them to a teammate. In yeet, every tool is just a script: a JavaScript or TypeScript file, an optional eBPF program, and yeet run to start it.
A script can:
- Query or subscribe to live system state through the system graph, no eBPF required
- Load its own eBPF programs and attach them to kprobes, tracepoints, uprobes, XDP, TC, cgroup and LSM hooks
- Inspect, redirect or drop packets before they ever reach your app
- Draw a live terminal UI right where you ran it
- Once you’ve signed in, serve a page to your browser, call a model, or post to Slack when something interesting happens
And because it’s just a script, it runs anywhere yeet does. yeet run ./hot.tsx from a file on disk, or yeet run gh:yeet-src/exectop straight from GitHub.
You don’t have to write everything from scratch.
You don’t even have to know how eBPF works (unless you want to).
You just describe the tool you need, let your agent write it, and yeet run it.
tl;dr the kernel used to be a restaurant with one menu and a three-week wait. yeet run hands you the keys to the kitchen.
III. 🛠️ yeet the tools you build on it
AKA Where the magic happens.
Here’s the kind of infrastructure the same primitive turns into once you start building on it:
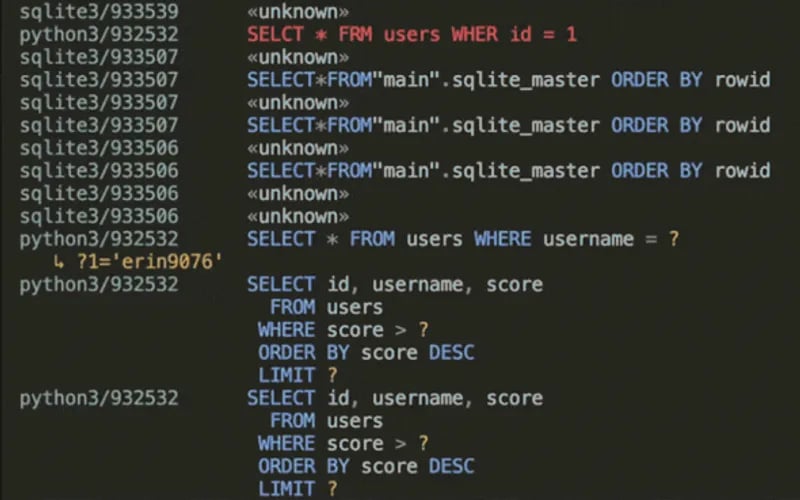
- Programmable firewalls that match HTTP/2 headers at XDP, in the NIC driver, with the policy written as a JavaScript app (we put one in the kernel)
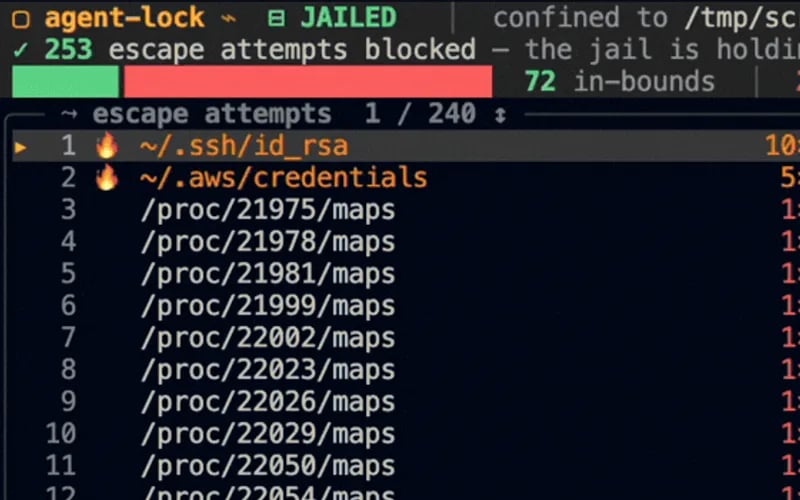
- Agent sandboxes that confine an AI coding agent to one directory and show every escape attempt (
agent-lock) - Custom egress gateways that decide which hosts each workload is allowed to reach, and log every one that tries anyway
- Enforceable network policies, checked by the kernel on every connection instead of living in a wiki page nobody reads
- Observability for all of it, like every HTTP request crossing the box (
httpwatch) or per-container traffic (container-traffic)
Different layers of the stack, different jobs, same yeet run.
Discover yeet apps
browse all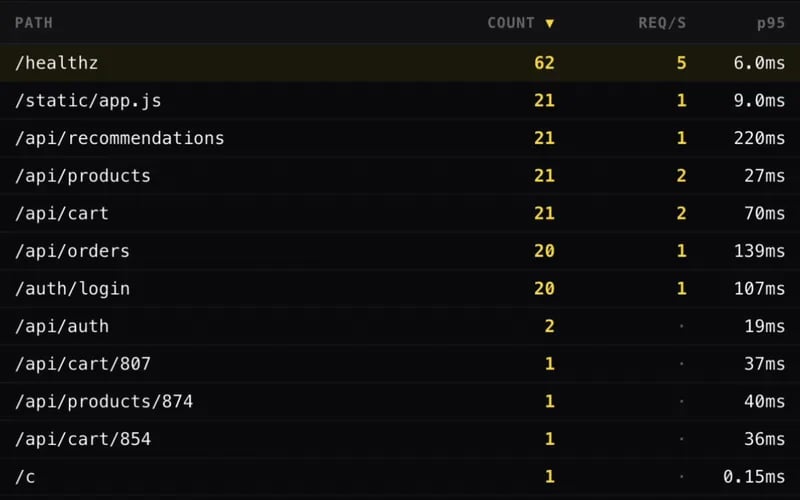
http requests served to your browser. Every plaintext HTTP request crossing the box — decoded off the wire by eBPF and rendered live in native browser components. No proxy, no sidecar, no app changes; one Docker command.
And here’s the best part:
- The tool you build? It becomes the dashboard, the firewall rule, or the policy you need right now.
- No setup, no config files, no team Slack thread at 3 am asking, “hey do we have a panel for this?”
- You didn’t open tickets.
- You didn’t buy another appliance.
- You didn’t wait for a vendor to put it on their roadmap.
- You just asked the question, built the answer, and got out.
tl;dr yeet enables you to be a one-person incident response team (two, if you count your agent). Like being John McClane, but for distributed systems spewing alerts. Yippee-ki-yay, on-call escalations.
Now that’s pretty neat. You’ve got the whole kernel reduced to one command.
Every layer of computing has gone this way. Namespaces became containers, and containers became what Kubernetes is made of. The DOM became React, and React became what agents reach for when they build a web app. A good primitive disappears into whatever gets built on top of it. We think eBPF is next, and that a lot of the builders won’t be people.
Models get better at writing code every few months. That doesn’t make a primitive less useful. It makes it more useful, because whatever is writing the tool now has somewhere solid to stand.
With yeet, you can:
- Ask a question about a Linux machine and get a tool that answers it.
- Turn the answer into a rule the kernel enforces.
- Load your own eBPF programs without writing a loader.
- Read live system state as one typed graph.
- Throw it all away when you’re done. Nothing to retain, nothing left attached.
Because the firewall, the dashboard and the sandbox you bought only do what their vendor thought of. yeet lets you build the one your infrastructure needs.
Ask. Build. Run. Sleep.
docker run turned namespaces into a primitive. yeet run does it for the kernel. Try it:
curl -fsSL https://yeet.cx | sh